A storefront is not one codebase. It is your code plus analytics, plus the chat widget, plus the tag manager, plus whatever the tag manager loaded this morning. You reviewed those vendors once, at the point you added them. They have shipped code to your customers every week since, and nobody read any of it.
That is not a hypothetical attack path. It is the ordinary way a payment page gets compromised: not a break-in at the store, but a change to something the store already trusted.
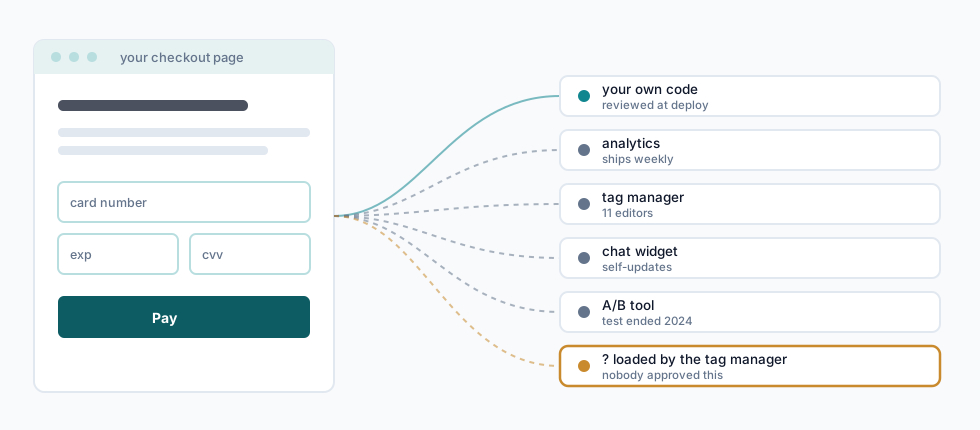
A first inventory on a mid-market store turns up more than anyone expects. The last row is the one nobody approved.
Two problems, depending on what you run
If you sell things — the checkout
Script inventory, change detection, and the evidence you need for PCI DSS 4.0's script-management requirements. Every script that executes on a payment page, what it was authorized to do, and what changed.
If you run a marketplace or an app — the accounts
Credential stuffing, seller-account takeover, and API abuse at a scale where blocking by IP stopped working years ago. Built for platforms where the attacker already has a valid account.
Why most teams find out late
Most skimming code reaches a storefront through a vendor's update, not through a break-in at the store. So the tooling that watches your perimeter never fires, your dependency scanner never sees it — the script is loaded at runtime, from someone else's domain, into your customer's browser — and the first real signal is a chargeback pattern weeks later.
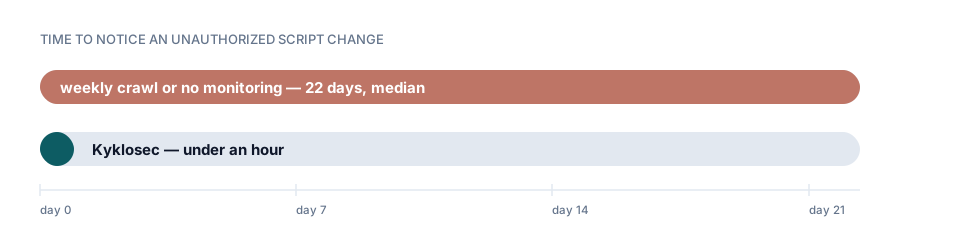
Periodic scanning does not close that gap. A weekly crawl finds a change up to seven days after it happened, and the people who write skimmers know what a weekly crawl looks like. Kyklosec is named for kyklos, the Greek for cycle, because continuous is the entire point: the check runs in the session, not on a schedule.
What you get on day one
- A complete inventory of what actually executes on your checkout, which for most stores is longer than the list anyone expected.
- A baseline, so "changed" means something specific rather than "looks different".
- Alerts that name the script, the vendor, and what the change did — not a severity score.
Where teams usually start
Most people arrive with a situation rather than a product in mind — a QSA asked a question, or peak season is coming, or a metric went up and turned out to be card testing. The solutions pages start from the situation: online retailers, marketplaces and apps, PCI DSS 4.0, and peak season.
It is the fastest way to know your checkout is clean.